Digital ID Explained: Pros, Cons, and “Should I get the Trident ID card?”

PURPOSE

I continue to receive countless questions from various walks of Bajan society about the Trident ID card and the national digital ID program. This is stark evidence that the Government of Barbados HAS NOT done an adequate and effective job of alleviating the concerns of the public. As such, I wanted to clarify once and for all the pros and cons of digital ID systems, and answer the million dollar question I am repeatedly asked, “Should I get the Trident ID card?”

INTRODUCTION

Digital identity (ID) has become the topic of the moment in Barbados, given the government’s poor implementation, failure to address the fears and anxieties of the public, and generally ineffectual communication to the average person on the street as to why they need digital ID and what value it will bring to their lives. The government has set out to provide a single digital identity to all residents/citizens through the collection, storage, and use of their biographic data (e.g., name, address, date of birth, gender, national registration number, etc.) and possibly their biometrics (e.g., fingerprints, iris scans, facial scans, etc.) as the primary means of establishing and verifying their identity. They will achieve this through a legally mandated, centralised national digital ID system.

Governments, international organizations, and multilateral banks (e.g., International Monetary Fund, World Bank, etc.) argue that digital ID systems provide benefits such as more effective and efficient delivery of government services; poverty reduction and welfare programs; financial inclusion through better access to banking and other products/services; minimise corruption; and preservation of national security interests. Multilateral banks are providing significant funding to developing countries to implement digital ID. In some cases, they’re even making the implementation of digital ID systems a ‘condition’ of loan agreements.

Critics maintain that digital ID systems may actually not guarantee more effective access to social and economic benefits, enhance service delivery, or improve governance, while at the same time, they raise serious issues, including worries about how they are developed and managed; social exclusion and discrimination; privacy and data protection; cybersecurity; and major risks for human rights. With regards to human rights, they threaten the right to privacy, freedom of movement, freedom of expression, and other protected rights. Additionally, since they usually involve the creation and maintenance of centralised databases of sensitive personal data, they are also prone to breaches by hackers or abuse/misuse by government institutions. These issues may lead to digital IDs becoming widespread tools for identification, surveillance, persecution, discrimination, and control, especially where identities are linked to biometrics and made mandatory. 

For a more detailed explanation of both sides of the debate, please see below the PROS and CONS related to digital ID systems.

PROS

Easier access to services: digital ID systems can enable more efficient digital transformation across the local economy and increase Barbados’  participation in the global digital economy, especially given that many transactions – local and international – require personal identification. With Barbadians presented with less obstacles to prove their identity, commercial activities (including e-commerce) and government services (including e-government) become more accessible and effective.

Faster and cheaper transactions: the use of digital ID can allow for reductions in costs and response times, resulting in speedier execution, less red tape, and the availability of more responsive and relevant services. The quickness and trust with which a person’s identification can be verified allows for cheaper and more efficient interactions for all involved.

Fraud reduction: digital ID systems can offer several benefits in terms of online security, thus reducing the occurrence of online scams, fraud, and personal data breaches. A number of countries that have implemented digital ID have experienced significant decreases in fraud, saving them tens and even hundreds of millions of dollars.

The graphic below outlines several ways in which digital ID can be used based on the roles played by organizations and individuals (Source: McKinsey).

The four (4) main areas of direct economic value for individuals have been identified as increased access to financial services, improved employment opportunities, greater agricultural productivity, and time savings. The five (5) highest sources of value for institutions – both the private and public sectors – are cost savings, fraud prevention, increased revenues from goods and services, improved employee productivity, and higher tax revenues.

CONS

Privacy and security: digital ID systems process billions of data points of our private information, regularly without our consent or knowledge. This information can include biographic details (NGN, date of birth, gender), biometrics (facial recognition, iris scans, fingerprints), banking and transactional data, and location-based info when digital ID is used for example in public transportation (the government has expressed plans to use the Trident ID for cashless payments on buses). The centralisation of so much data, excessive sharing of personal data without user consent, inability to control your personal data, exposure to cyber attacks and data breaches, and in worst case scenarios – mass surveillance by corporations and governments – are all issues which show the potential negative impact of digital ID.

Discrimination, biases and exclusion: the Barbados Digital Identity Act has a number of clauses which generate concerns about discrimination and exclusion. The Act states in several places that the digital ID will be required for persons to be added to the register of voters, to vote in elections, to access public and private services, and to obtain a driver’s license. There are no provisions in the Act for mandatory accessibility features in the digital ID and related services. As such, persons with disabilities may be excluded (e.g., the Trident ID website currently DOES NOT have several accessibility features for the disabled). Digital ID technologies are also at the end of the day developed by humans, and through poorly designed algorithms and data analytics, can reinforce their biases. Discrimination against key communities such as immigrants, LGBTQ+, homeless, and the disabled, among others have been highlighted in many digital ID related studies globally.

Technical errors: unintended consequences can occur that lead to restricted access to critical services (e.g., failures in authentication at points of service with no redundancy; websites that aren’t user friendly or stable; duplicate or inaccurate records; inability to add essential information; or the lack of reliable technical support, etc.). The government must fully consider availability risks and identify user-centric and privacy-enabling solutions to mitigate them. In African and Asian countries, numerous instances of technical errors were uncovered which presented citizens with major challenges.

Deployment challenges: five key problems exist, which are the lack of funding to maintain secure cyber systems and to hire or retain critical human resources to administer them; unequal access to mobile Internet and smartphones – the technology with the most potential to drive the uptake of digital ID; dependency on a specific technology or vendor; low trust in government; and the difficulty of rolling out in rural areas.

SHOULD YOU GET THE TRIDENT ID CARD?

As I have stated before, my concern is not particularly with the Trident ID card. The card is only one small piece of the overall digital ID ecosystem. My biggest concerns are as follows:

Poor legislation underpinning the digital ID system: Digital ID must be supported by a legal and regulatory framework that supports trust in the system, prevents abuse such as warrantless and disproportionate surveillance, guarantees data privacy and security, prevents discrimination, and maintains provider (government and corporations) accountability. This includes laws for digital ID management along with laws and regulations for e-government, privacy and data protection, computer misuse, data sovereignty/localisation, electronic transactions, limited-purpose ID systems, accreditation of participants, and freedom of information, among others. Unfortunately, a number of these laws are not available in Barbados at this time, and where they are, the language is problematic, enforcement is deeply lacking, or the legislation is outdated.

Government’s atrocious record in terms of protecting IT systems and the personal data privacy of individuals: The Government of Barbados DOES NOT have the resources (people, processes, or technologies) to secure complex IT systems and provide consistent privacy-enabling solutions. If they did, there would not be so many successful cyber-attacks and data breaches of government online systems in recent years (e.g., Queen Elizabeth Hospital, Ministry of Information and Smart Technology, Immigration Department, Barbados Police Service, and many others). Until government invests significantly in building their capacity in these areas, their IT systems and the personal data of Barbadians will be AT RISK.

The communication (or lack of) by government addressing the public angst around their digital ID program: Government has not effectively articulated the benefits of digital ID, its value to the average person on the street (in real and meaningful terms), its potential disadvantages and risks, what they are doing to manage these risks, and what Barbadians can do to protect themselves. Instead they have chosen to evade questions, avoid public discussion with experts involved, and turn their resources towards attacking private citizens who are expressing concerns.

In 2018, I conducted a European Union (EU) cybersecurity assessment for the the Government of Barbados. In the report, I clearly stated:

Trust in the Internet and in the use of online services is critical to developing a thriving local Internet economy and to participating widely in the global digital economy. Low trust in the Internet, e-government services, and e-commerce services hampers the government, businesses and consumers from fully taking advantage of all the economic benefits the Internet has to offer. Given the high fixed broadband and mobile data penetration rates in Barbados, this is especially concerning.

European Union Consultancy to Develop a Government Cybersecurity Assessment and Strategic Roadmap – Cybersecurity Assessment Report (Authored by Niel Harper)

From 2018 to this present day, the government has failed to address the low levels of trust or their lack of expertise in delivering secure and privacy respecting IT solutions, all of which are undoubtedly preventing them from delivering their digital transformation and modernisation agenda (including the implementation of the digital ID).

Ultimately, Barbadians need to decide for themselves if the value of obtaining the Trident ID outweighs the associated risks. I cannot make this decision for anyone. All I can do is educate and build awareness, and try to put some pressure on the government to be more accountable and take greater responsibility for protecting citizens from the negative effects of digital ID, mass personal data processing, cyber attacks and data breaches, human rights violations, online fraud, and other harms resulting from widespread government use of information and communication technologies (ICTs).

ADDITIONAL RESOURCES

FACT CHECK: The Electoral and Boundaries Commission’s Response

Why the Barbados Election Least Data Leak is Problematic – And How It Could Have Been Prevented

Comments on the National Identity Management System Act

Too Many Unanswered Questions: The Barbados National Digital Identification

Creating a good ID system presents risks and challenges, but there are common success factors
What is a digital identity ecosystem?

Understanding the risks of Digital IDs

12 CISO Resolutions for 2022

At the beginning of January, my peers and I shared our security and privacy resolutions for 2022 with CSO Online. The full article can be found here on their website.

However, I wanted to further elaborate here on my plans for privacy and security across the enterprise this year.

I have a couple of resolutions for the upcoming year. Firstly, I want to focus more energy and resources on privacy and data. My second resolution is to refine and enhance the control framework around third-party risk management. In third place, but definitely not of lesser importance, is improving my enterprise’s protection against ransomware. The next resolution on my list is continuing to advocate the importance of email security to every business leader I meet; I am specifically referring to Domain-based Message Authentication, Reporting and Conformance (DMARC), DomainKeys Identified Mail (DKIM), and Sender Policy Framework (SPF). Finally, I want to gain more control over ‘shadow IT.’

With regards to privacy and data, it’s not only about responding to growing demands from GDPR and other national and regional privacy regulations. It’s just good practice to get a solid handle on where business-critical data assets reside and how this data moves inside and outside of your organization, ensuring that you have adequate and effective controls to prevent data leakage and privacy rights violations (and of course avoid fines). Over 55% of data breaches are now caused by a third-party, so ensuring that I have an efficient, standardized approach for assessing third party risk will most definitely reduce privacy and security exposures from vendors, services providers and even contractors. Ransomware continues to increase in terms of prevalence and severity, so a strong prevention and response strategy is key to operational, financial, and reputation risk reduction. Email security in some form has been around since the early 2000s, and yet less than 35% of companies have implemented DMARC, DKIM and SPF. The value of these technologies in combating brand impersonation, reputation damage, and phishing attacks can’t be emphasized enough. Shadow IT in basic terms means that you’ve lost control and visibility into your IT environment, and if you can’t account for IT assets, you can’t protect them.

My approach to privacy and data governance is premised on user/cultural awareness, end-to-end risk assessment, detailed records of processing activities, effective incident response, strong security controls, and building capabilities to integrate ‘privacy by design’into the CI/CD. I plan to move away from using spreadsheets and manual processes to manage third-party risks, and instead leverage best-of-breed software tools that analyze, track, and minimize risks arising from supply chain exposures. With ransomware, my objective is to incorporate identity and access governance, multi-factor authentication (MFA), advanced honeypots, endpoint detection and response (EDR), and multi-tiered backups (3-2-1 strategy) into a cohesive ransomware prevention strategy. As it pertains to email security, my focus is less about my own shop (we’re already there) and more about assisting my peers and small to medium enterprises (SMEs) in properly setting up DMARC, DKIM, and SPF. Preventing shadow IT begins with enhancing usability and eliminating risky workarounds by removing the hindrances that foster them (i.e., being more agile in addressing discrete stakeholder requirements in close collaboration with the IT function).

Why the Barbados Election List Data Leak is Problematic – And How it Could Have Been Prevented

On 27 December 2021, the Prime Minister of Barbados Mia Amor Mottley scheduled a snap election for 19 January 2022.

On 29 December 2021, a full data dump of all eligible voters in the country was published by the Government of Barbados on the open Internet. This occurred largely because the Representation of the People Act 13(1) states “The [Electoral] Commission shall cause to be prepared and shall publish not later than the 31st day of January in every year a register of electors for each constituency and a register of foreign service electors entitled to vote at any election.” 

In the past, this list was made available in somewhat controlled environments to be queried by election officials, candidates, voters, etc. to ensure that elections accurately reflected the will of the people (in most all cases it was usually printed and held at libraries, constituency offices, polling stations, etc. to be reviewed by interested parties). To limit congregation of individuals in the previously mentioned locations during COVID-19 times, it was decided to publish the full voters list on the Internet to ensure access for all.

The 5250-page list contains approximately 250,000 individual records with the below personally identifiable information (PII). *

  • Last Name
  • First Name
  • National Registration Number (similar to a Social Security Number in the United States)
  • Gender
  • Date of Birth
  • Residential Status
  • Constituency (Voting District)
  • Home Address

* The total population of Barbados currently hovers around 290,000 persons.

Instead of this data being restricted to a few thousand persons in Barbados, it was now accessible by all 4.6 billion Internet users, exposing 250,000 Barbadians to increased risks of data misuse and abuse, fraud, identity theft, and other financial and reputation risks. The information was quickly downloaded and posted on Reddit and a number of hacker/fraudster sites on the Dark Web, making it perpetually available to malicious actors. There is also a high physical risk to individuals with regards to stalking, home invasions, robberies, rape, etc.

PII, also referred to as personal data, covers a wide variety of information that can identify a living individual. If a piece of information is unique to that person, it can lead back to them in several ways, and it is private and needs to be protected with the greatest care.

Why Does Personal Data Need to be Kept Safe?

The reason this type of information requires protection is that it can be used to commit fraud or to steal an individual’s identity.

Depending on what a thief is trying to accomplish, he will need different types of information. To open specific accounts all that is needed is an email address, while in other cases an individual’s name, address, date of birth, a national registration number, and other information may be required.

It’s also critical to note that accounts of all types can be opened over the phone or via the internet without having to physically visit a location for your identity to be verified. This provides opportunities for criminals with appropriate stolen information to open bank accounts, enter into contractual agreements, or make claims using someone else’s information or identity.

If a criminal is fraudulently using your information, you might not even know it. They may not use the credit card you already own to make purchases (in which case you might catch them by looking at your purchase history). Most often, criminals open up new, separate accounts using the victim’s information, leaving the victim unaware of the damage that is being done until years after the fact. In that time criminals can rack up a lot of debt using your identity.

How Can Identity Thieves Use Your Personal Data?

There are several ways which identity thieves can use your personal data, including but not limited to the following:

  • Open a new credit card account.
  • Create fake social media accounts with your identity (e.g., Facebook, Twitter, Instagram, etc.).
  • Take out a commercial bank loan.
  • Obtain and use your debit card to withdraw funds.
  • Change your billing address so your bills will no longer be delivered.
  • Obtain expensive medical care or procedures.
  • Open new utilities accounts in your name (e.g. electricity, water, natural gas, etc.).
  • Obtain a mobile phone service.
  • Open a bank account, obtain a cheque book, and write bad checks.
  • Obtain a new driver’s license or national ID.
  • Use your information when arrested or in a court action.
  • Engage in bullying, stalking, harassment or otherwise cause fear.
  • Inflict severe reputation damage.
  • Combine it with additional data gathered from the Internet (e.g., Google search, Facebook, Instagram, LinkedIn, etc.) to create even more detailed profiles of individuals.

How Long Does It Take Fraudsters to Use Stolen Personal Data?

In 2017, the Federal Trade Commission (FTC) in the United States demonstrated how criminals can use your personal information within minutes. The FTC developed fake personal data and posted it on a website that hackers use to make stolen information available. It took a mere nine (9) minutes for the fraudsters to access the information, and over 1,200 attempts were made to access email, credit card and payment accounts. The research confirms how valuable personal information is to identity thieves, and if they can gain access to it, they will most definitely use it.

What Should the Government Have Done Instead?

While it’s not an exhaustive list, below are some of the key steps the government should have taken.

From a technology perspective, a searchable database should have been published on the Government Information Service (GIS) portal, where individuals could use personal data which they already knew to confirm that they were on the voters list. The full database could have been provided to election officials and campaign managers using a digital rights management (DRM) solution to control access and distribution of the document. 

The Data Protection Act was approved by Parliament in July 2019 and came into force in March 2021. This statute introduces a strong privacy and data protection regime in Barbados, and its wide-reaching impact on overall data governance across sectors and industries should have triggered key updates to existing legislation, processes and operational guidelines (including the Representation of the People Act and any other legislation involving personal data processing). And this doesn’t even address the urgent need for broader legislative reforms in the country. There are way too many outdated pieces of legislation which are incompatible with progressive changes in technology, changing community awareness, changing community values, and changing expectations of the legal system.

Appropriate funding should be allocated to the Office of the Data Protection Commissioner to better equip them in investigating and monitoring data breaches and providing other types of regulation involving the public sector. Additionally, these financial resources can be used to deliver privacy awareness training to educate government personnel on how to protect individual privacy in their daily work. Simultaneously, a public campaign should be started to achieve broad public awareness on all issues related to the Data Protection Act and the new legal framework created. The Office of the Data Protection Commission is severely under-resourced at present, making it virtually impossible to implement and enforce the Data Protection Act, which focuses largely on preventing exactly these types of data leakages. For example, adhering to the principle of data minimisation would have significantly reduced the risk and impact of publishing the entire voters list. By this I mean the narrowing of data collection and processing to strictly what is needed – In this case, there is absolutely no reason to publicly release the National Registration Number (NRN) and Date of Birth of all eligible voters.

Why the Electoral and Boundaries Commission (EBC) is Dead Wrong

The Electoral and Boundaries Commission (EBC) has strongly (and wrongly might I add) defended its decision to publish the voters list online. Their position is that “We are obligated to publish the list now electronically so that more people can have access to it.” Chairman of the EBC Queen’s Counsel Leslie Haynes also maintains that “ID numbers are not private” and made reference to them “being published before the introduction of the digital age in public libraries, rum shops, the electoral office and other spaces.” Because a law states that you must publish information electronically doesn’t mean you should make it accessible to 4.6 billion Internet users (including hackers, fraudsters and other cyber criminals). There are numerous laws in Barbados that are outdated, poorly drafted, contradictory to other laws, and incompatible with existing technology – Should we follow them all to the letter or do we comprehensively update them to be more fit for purpose? Moreover, there are numerous technology solutions available for publishing said data online in a controlled manner to reduce the overall risk and exposure. And if they are not at fault, why did government officials remove the voters list from the public websites?

Finally, national registration number (NRN), date of birth (DOB) and home address are all private information, and there are established technical standards, privacy principles, and national laws or treaties around the globe that assert as much. From a data minimisation perspective, the requirements of the law could have been satisfied without including NRN and DOB.

Where online can you find the social security numbers (SSNs) for all eligible voting Americans? What about the passport numbers or driver’s license numbers for all voting Canadians? What about the national ID numbers for all voters in France, Denmark, Switzerland, Germany, etc.? The answer is NOWHERE!

[UPDATE] Sunday, 2 January 2022 – I have amended the original blog post in response to the EBC’s staunch defence of their decision to publish the voters list on the open Internet.

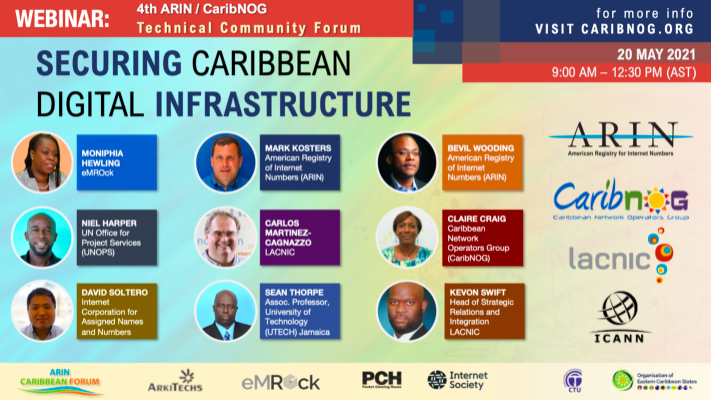
ARIN/CaribNOG Technical Community Forum

The COVID-19 pandemic continues to impact networks, economies and societies across the Caribbean. More than ever, keeping critical systems secure, resilient, and accessible is a collective responsibility. This year’s Forum presented the opportunity for participants to understand the role the American Registry for Internet Numbers (ARIN) and other Internet development focused organizations play in supporting critical Internet Infrastructure in the Caribbean. It also facilitated the networking of people necessary to truly support and strengthen our technical community in the region.

ARIN has been collaborating closely with CaribNOG, a volunteer-based network operators’ community, to strengthen technical capacity in the region. This forum assembled some of the leading experts in the region and from around the world to address the fourth staging of our Technical Community Forum.

As the first featured speaker, the topic of my address was ‘Global Cybersecurity Trends and Implications.’ I first discussed the global shortage of cyber security personnel and encouraged the Caribbean to focus on the development of cybersecurity experts to support local, regional, and global demand (and also as a key element of national cyber workforce development). I also touched on other topics such as developing cybersecurity programs with constrained budgets, coordination and cooperation towards increase security resilience, and how to stay on top of developments in an increasingly complex threat landscape.

Many thanks to ARIN and CaribNOG for their invitation to speak!

Incoming ISACA Board Features Experienced Leaders, Diverse Backgrounds

Deeply humbled to have been elected to the incoming Board of Directors for the Information Systems Audit and Control Association (ISACA).

The organisation has been instrumental in my career development and success, and I am looking forward to collaborating with this brilliant group of professionals and serving the dynamic and diverse ISACA community.

You can view the official announcement here: https://bit.ly/2QkW5S6

CARICOM Public Law Podcast – Cybersecurity and Digital IDs

Season 1 Episode 8 of the CARICOM Public Law Podcast is now available!

In this episode of the podcast, I spoke to the hosts about the technological, legal, ethical, economic, and business issues surrounding the Barbados government’s decision to introduce a new digital identification management system.

Special thanks to Rico J. Yearwood and Mequissa Baptiste for inviting me to share my perspectives on their platform.

Click on this link to tune in and listen!

Facts vs Fiction: What’s the ‘Right to be Forgotten’ Really About?

There’s still a vigorous debate going on about the ‘right to erasure’, also referred to by some as ‘the right to be forgotten.’ Its detractors strongly argue that it is tantamount to censoring lawful and factual information, and is dubious on principle. They also believe it to be deeply flawed as a method of protecting privacy.

I believe those to be simple-minded positions. The ‘right to erasure’ allows for data subjects to have their data scrubbed when it is no longer necessary for the purpose an organization originally collected it. It is also key when there is no overriding legitimate interest for an organization to continue with the processing. It also protects an individual when their data is being processed unlawfully or when an organization has to adhere to a court ruling.

To be more specific, Article 17 of the GDPR outlines the conditions under which the right to be forgotten takes precedent. An individual has the right to have their personal data erased when:

  • The personal data is no longer required for the original purpose an organization collected or processed it;
  • An organization is relying on an individual’s consent as the lawful basis for processing the data and that consent is withdrawn;
  • An organization is relying on legitimate interests as its justification for processing an individual’s data, the individual objects to this processing, and there is no overriding legitimate interest for the organization to continue with the processing;
  • An organization is processing personal data for direct marketing purposes and the individual objects to this processing;
  • An organization processed an individual’s personal data unlawfully;
  • An organization must erase personal data in order to comply with a legal ruling or obligation; and
  • An organization has processed a child’s personal data to provide them with specific information services.

However, there are several instance which override the right to erasure:

  • The data is being used to exercise the right of freedom of expression and information.
  • The data is being used to comply with a legal ruling or obligation.
  • The data is being used to perform a task that is being carried out in the public interest or when exercising an organization’s official authority.
  • The data being processed is necessary for public health purposes and serves in the public interest.
  • The data being processed is necessary to perform preventative or occupational medicine. This only applies when the data is being processed by a health professional who is subject to a legal obligation of professional secrecy.
  • The data represents important information that serves the public interest, scientific research, historical research, or statistical purposes and where erasure of the data would likely to impair halt progress towards the achievement that was the goal of the processing.
  • The data is being used for the establishment of a legal defense or in the exercise of other legal claims.
  • Furthermore, an organization can request a “reasonable fee” or deny a request to erase personal data if the organization can justify that the request was unfounded or excessive.

As is evident by a deeper look at the GDPR, a number of factors contribute to successfully having your data erased. Each request has to be assessed individually, the request must not interfere with other fundamental rights, it shouldn’t take precedent over the public interest, or countermand law enforcement requirements, etc. It is NOT a lawful reason to erase history or hide data about yourself that is embarrassing, and it doesn’t generally allow you to obscure your criminal past.

That being said, the issue of outdated and irrelevant information remaining indefinitely online is one that law has not effectively addressed (especially in the Internet Age). And it’s a dilemma that is predominantly more harmful for those who aren’t public figures — the folks who are in greater need of privacy protections from the law.

The Impact of the GDPR on the Hospitality Sector

Today I held a General Data Protection Regulations (GDPR) awareness seminar for members of the Barbados Hotel and Tourism Association (BHTA).

With regards to data security, there are few sectors more vulnerable to data-related threats than the hospitality sector. The volume of processed personal and credit card information being handed over to hotels, restaurants, etc. on a daily basis makes the sector extremely vulnerable. With the enforcement deadline having passed on 25 May, several companies in the sector have not updated their data protection processes, and are at risk for large financial penalties.

The seminar touched on key areas such as the following:

  1. Major Differences between the Data Protection Directive 95/46/EC and the GDPR
  2. Overall readiness across the hospitality sector
  3. Capturing and using personal data going forward
  4. Consent and contextual use of personal data
  5. How the GDPR affects repeat business and email marketing
  6. How the GDPR affects third-party data processors
  7. The rights of data subjects under the GDPR
  8. The difference between ‘personal data’ and ‘sensitive data’, and how they should be treated
  9. Other key aspects of the GDPR such as the Data Protection Officer (DPO), Data Protection Impact Assessments (DPIA) and ‘privacy by design’
  10. How to update strategies for websites, data governance, and marketing to become GDPR compliant

My takeaway from this session was that many businesses — small to large — have not made any steps to align their operations and processes with the requirements of the GDPR. Several others are defiantly refusing to address privacy and data protection within their organizations. However, what was gratifying is that I received a torrent of emails in the hours and days after from hoteliers, many of them eager to engage subject matter experts (SMEs) to assist in improving their control framework to meet the rigorous demands of the GDPR. Hopefully, this interest and willingness to improve is sustainable. There’s a lot of work to be done!


The Role of Governments in Ensuring a Consistent Legal Framework for Internet Governance

multi

The Internet is not an ethereal or otherworldly thing, and existing laws in the offline world are applicable to “cyberspace”. The Internet is for all intents and purposes a tool for making data available and for accessing it. But unfortunately, it is a tool that can be used by individuals and groups to conduct illegal activities. Similar to the offline world, governments have a social responsibility to develop laws that address criminal and illegal behaviors online. Hence, ensuring that an adequate and effective legal framework exists is an important role for governments.

Data protection and privacy

Data protection and privacy are high on top of the list of important legal issues, especially given that people are increasingly storing more of their data online and large amounts of data are collected, searched and manipulated electronically. In the EU, the Data Protection Directive 95/46/EC was established to provide a regulatory framework to guarantee secure and free movement of personal data across the national borders of the EU member countries, in addition to setting a baseline of security around personal information wherever it is stored, transmitted or processed.[1] However, although these laws conform to the Directive in terms of basic concepts and principles, they tend to be slightly different in many relevant details. The differences in the way that each Member State implemented the law have led to inconsistencies, which create complexity, legal uncertainty and administrative costs. This affects the trust and confidence of individuals and the competitiveness of the EU economy.

In January 2012, the European Commission (“the Commission”) presented a proposal for a General Data Protection Regulation (GDPR) to replace Directive 95/46/EC.[2] On 21 December 2015, the European Parliament and Council reached agreement on the data protection reform proposed by the Commission. The Regulation updates and modernizes the principles enshrined in the 1995 Data Protection Directive to guarantee privacy rights. It focuses on reinforcing individuals’ rights, strengthening the EU internal market, ensuring stronger enforcement of the rules, streamlining international transfers of personal data and setting global data protection standards.

Responses to the reforms haven’t been all positive. Bird & Bird lawyer Gabriel Voisin strongly maintained that, “The text adopted at today’s plenary session of the European Parliament is over-prescriptive. It will hamper Europe’s ability to take advantage of new ways of using data. This will put Europe at a disadvantage to other parts of the world that are embracing the new technologies”.[3] Christian Toon, Head of Information Risk at Iron Mountain, told SCMagazineUK.com that,“While consumers will welcome the fact that the European Parliament has voted through the EU’s first major overhaul of data protection legislation since 1995, many European businesses will be feeling nervous… The reality is that many remain underprepared… Businesses that fail to address the issue now not only run the risk of significant financial penalties in the near future, but may also risk serious reputational damage that will make customer retention more complicated.”[4]A number of other subject matter experts had similar comments.

Whether these criticisms are real or perceived, they represent a failed attempt at consensus between the European political establishment and its stakeholders. This has happened due to the fact that the GDPR was agreed to without adequate consideration of the 4000 amendments tabled by stakeholders, and the lack of political agreement among Member States in the European Council.[5] Consensus building is a critical aspect of Internet governance. The input of committed and informed stakeholders in decision-making processes, in their substantive roles and responsibilities, is imperative to verifying that outcomes are both effective and accepted. It also guarantees that diverse stakeholders can directly contribute to activities and are privy to their results. Consensus essentially facilitates solutions that meet the diverse needs of the Internet ecosystem, and moves the governance structure from top down to bottom up.

International Cooperation

The Internet is a cross-border platform and many of its legal and enforcement mechanisms necessitate international cooperation. The specific challenge posed by the cross-border aspect of the Internet is that activities that are legal in one country maybe illegal in another. Governments need to promote bilateral and inter-governmental agreements that support enforcement of the law. However, this is also the case in the offline world, where law enforcement can be bolstered through international cooperation between agencies. Governments have a responsibility to its citizens to cooperatively work together through international organizations such as the WTO, WIPO, Interpol and others in order to successfully combat illegal activity online.

A significant amount of international efforts have gone into the development of model laws for international cooperation and harmonization of cyber crime legislation. One example is the Council of Europe’s Convention on Cyber Crime.[6] The first of its kind, and the only effective global treaty on cybercrime, it was developed to address Internet and computer crime by harmonizing national laws, improving investigative techniques, and fostering international cooperation among nations. It tackles broad subject matter, dealing with infringements of copyright, computer-related fraud, child pornography and violations of network security. It also contains a series of powers and procedures, such as the search of computer networks and interception. There have been other attempts at creating model laws such as the Commonwealth Model Law on Cyber Crime and the Three ITU Model Laws – HIPCAR (Caribbean), ICB4PAC (Pacific Islands), and HIPSSA (Sub-Sahara Africa).[7] The Commonwealth Model Law was not widely adopted by many States, but the fact that much of its framework has been integrated into the ITU model laws has subsequently resulted in many of its requirements being applied to legislation in African, Caribbean, and Pacific (ACP) states.

Attempts at international harmonization of laws can be rife with challenges. In several instances, the omission of necessary provisions, defective language, fragmented drafting, integration of obscure and unsafe offenses and their variance away from and contradiction with established best practices inflict great damage to the objective of enhancing international cooperation against cyber crime. In many developing countries, the main challenge has been the unavailability of subject matter expertise in drafting legislation and regulations on cybercrime and electronic evidence. To solve this, government should look at broadening the communities with which they engage. Inviting the private sector and academia to participate in developing model laws can drastically improve the quality of legislative outputs. Additionally, seeking technical assistance from international organizations can also yield substantial benefits.

Conclusion

Internet governance, and the multistakeholder model it employs, is a reflection of the open and inclusive nature of the global Internet and has been an integral reason behind its amazing growth and success. Many governments have realized that deeper stakeholder engagement — including governments, businesses, civil society, the technical community and academic institutions — is the optimal approach to sharing knowledge, experience, competences and best practices when developing policies to address new opportunities and respond to emerging challenges.

Traditional models of governance that would institutionalize control over the Internet by governments and inter-governmental bodies cannot achieve these goals. Such rigid decision-making processes are unable to maintain pace with rapidly changing technological advancements that characterize the Internet, and the ever-evolving requirements of Internet users. Any attempts to superimpose traditional models would dampen innovation and constrain realization of the limitless benefits of an open Internet. It would risk stifling the dynamism that has allowed the Internet to deliver so many benefits and opportunities for economic growth and social welfare.

A revisionist approach to governments’ involvement in Internet governance should focus on overhauling the rules of engagement. These new rules would allow government officials to participate in architecting a new ‘distributed global governance framework’, with defined restrictions and in their macro-level role as public policymakers for Internet-specific matters. Notably, this function should not undermine the globally accepted norms and principles of Internet governance. Within a multistakeholder environment, all concerned parties could contribute to building a platform for further public policy elaboration. This could set the stage for the transformation of Internet governance into a truly international policy-making process. But in order for that to occur, we need visionary leaders, a change in mindset from control to collaboration, and strong political will.


How Secure is Barbados’ New Centralized Healthcare Information System?

health

Think about the following scenario for a minute:

A Caribbean government deploys a health information system (HIS) with the goal of improving the quality and coordination of patient care in the public service. For all intents and purposes, expert consultants from Europe and the USA are brought down to implement the system and to ensure that best practices for securing and protecting sensitive clinical data are used. The project is successfully completed, the consultants leave, and hand off day-to-day management of the system to the government’s IT staff.

The government has no overall IT security policies, procedures and guidelines to ensure that the system and the data housed in it continue to be secure and protected from malicious threats. There are no trained or experienced IT security experts on the government’s payroll. There are no data security standards enforced by the government. There is no data protection legislation in place to provide a control framework for protecting highly confidential healthcare data from being stolen by hackers or to prevent data from being accidentally lost or leaked.

Eventually, all these weaknesses together result in persistent compromises of the system by hackers, and all the private clinical data of the citizens of the country are posted on the Internet or otherwise made available for the world to see.

Does the above scenario make you shudder? I know it scares me to death.

The rest of this article will demonstrate how close to reality this is in the Caribbean region.

In the past week or so, the Government of Barbados informed the public of the launch of their Med Data healthcare information system (HIS) and electronic medical records (EMR) scheme. Let me first commend the government on this much-needed initiative to drive efficiency and improved standards of care in public healthcare. However, I have a number of grave concerns about the manner in which this project has been undertaken.

Data Protection Legislation

First of all, no data protection legislation has been discussed, ratified, and implemented through Parliament. Simply put, healthcare data must be processed fairly and with the consent of individuals, especially as it pertains to whom data is shared with and in what context. Legislation should address key areas such as mandatory data breach notifications, heightened enforcement, heavy penalties for breaches, and expanded patient rights. Moreover, any data protection legislation should have a broader scope and include the management and protection of data in areas outside of healthcare, namely banking, insurance and law enforcement.

In essence, data protection legislation would hold both private and public institutions accountable and liable for damages in the event of a security breach. It would also make it mandatory that all breaches are reported to the public so that data owners can take steps to protect their identities. And finally, it allows for heavy fines to be levied on any institution that fails to maintain strong security controls for data.

Data Security Standards

Secondly, there has been no development of data security standards to accompany the legislation and to provide best practice guidance for accessing, exchanging, transmitting, and storing healthcare data in a secure manner. On a broader scale, the Government has no risk management framework, no IT governance processes, and from an operational perspective, no procedures for responding to IT security incidents. There has been an initiative in play for some time now to create a Computer Security Incident Response Team (CSIRT), but it has stalled due to lack of resources (human and financial).

Given the number of security incidents that have occurred in the public sector over the last couple of years, one would think that government officials would be taking data privacy and security more seriously. Key systems at the Royal Barbados Police Force, Inland Revenue, and the Ministry of Foreign Affairs have been hacked in the last couple of years (and these are only the ones that have been made public or that the government are aware of).

But enough criticism of the government; let’s talk about solutions. There is no doubt that IT governance, risk and control (GRC) is an area that requires major attention from the Government of Barbados. The question is: How do we address these deficiencies?

Recommendations

For one, I would suggest that public officials engage local groups such as the Caribbean Cyber Security Center, Information Systems Security Association (ISSA) Barbados Chapter, Institute of Internal Auditors (IIA) Barbados Chapter, and the Barbados IT Professionals Association (BIPA) to assist them in building the necessary competences to improve the control framework and information security posture of the public sector.

Additionally, an online register of consultants should be established to allow the government to create a repository of world-class professionals — not only in IT, but across disciplines — who can assist them in delivering critical initiatives such as the Med Data project. All the expertise does not reside in Europe or North America. We have talent pools (of awesome individuals) across the Caribbean region that remain untapped.

Another area for improvement is around developing policy and legislation. There needs to be greater engagement of the general public and other interested parties in such processes — effective dialogue is constructive. Mechanisms such as e-participation or crowdsourcing can provide the government with a better understanding of the inherent risks, latent issues or knowledge gaps that may exist in program management and project delivery.

Finally, organizational management and intellectual capital development should be foremost on the minds of public officials. The leaders that we have elected need to think more strategic and create organizational structures that are agile and can respond expediently to the needs and demands of the people and address the key risks that the country is faced with. Centralized strategic planning and oversight of the tactical and operational aspects of IT are needed. Key positions such as the Chief Information Officer and Chief Information Security Officer must be defined and filled appropriately. Government employees have to be trained in disciplines such as project management, risk management, IT service management, business continuity, and cybersecurity.

The aforementioned recommendations are not meant to be a panacea. They are basic parts of a maturity model; one that will permit the government’s risk response mechanisms to evolve to better defend against the threats that exist and emerge. But more importantly, they are of critical importance to building trust in the e-government systems that the public are expected to use. They hopefully should also foster a risk-oriented philosophy that pervades throughout the public sector.