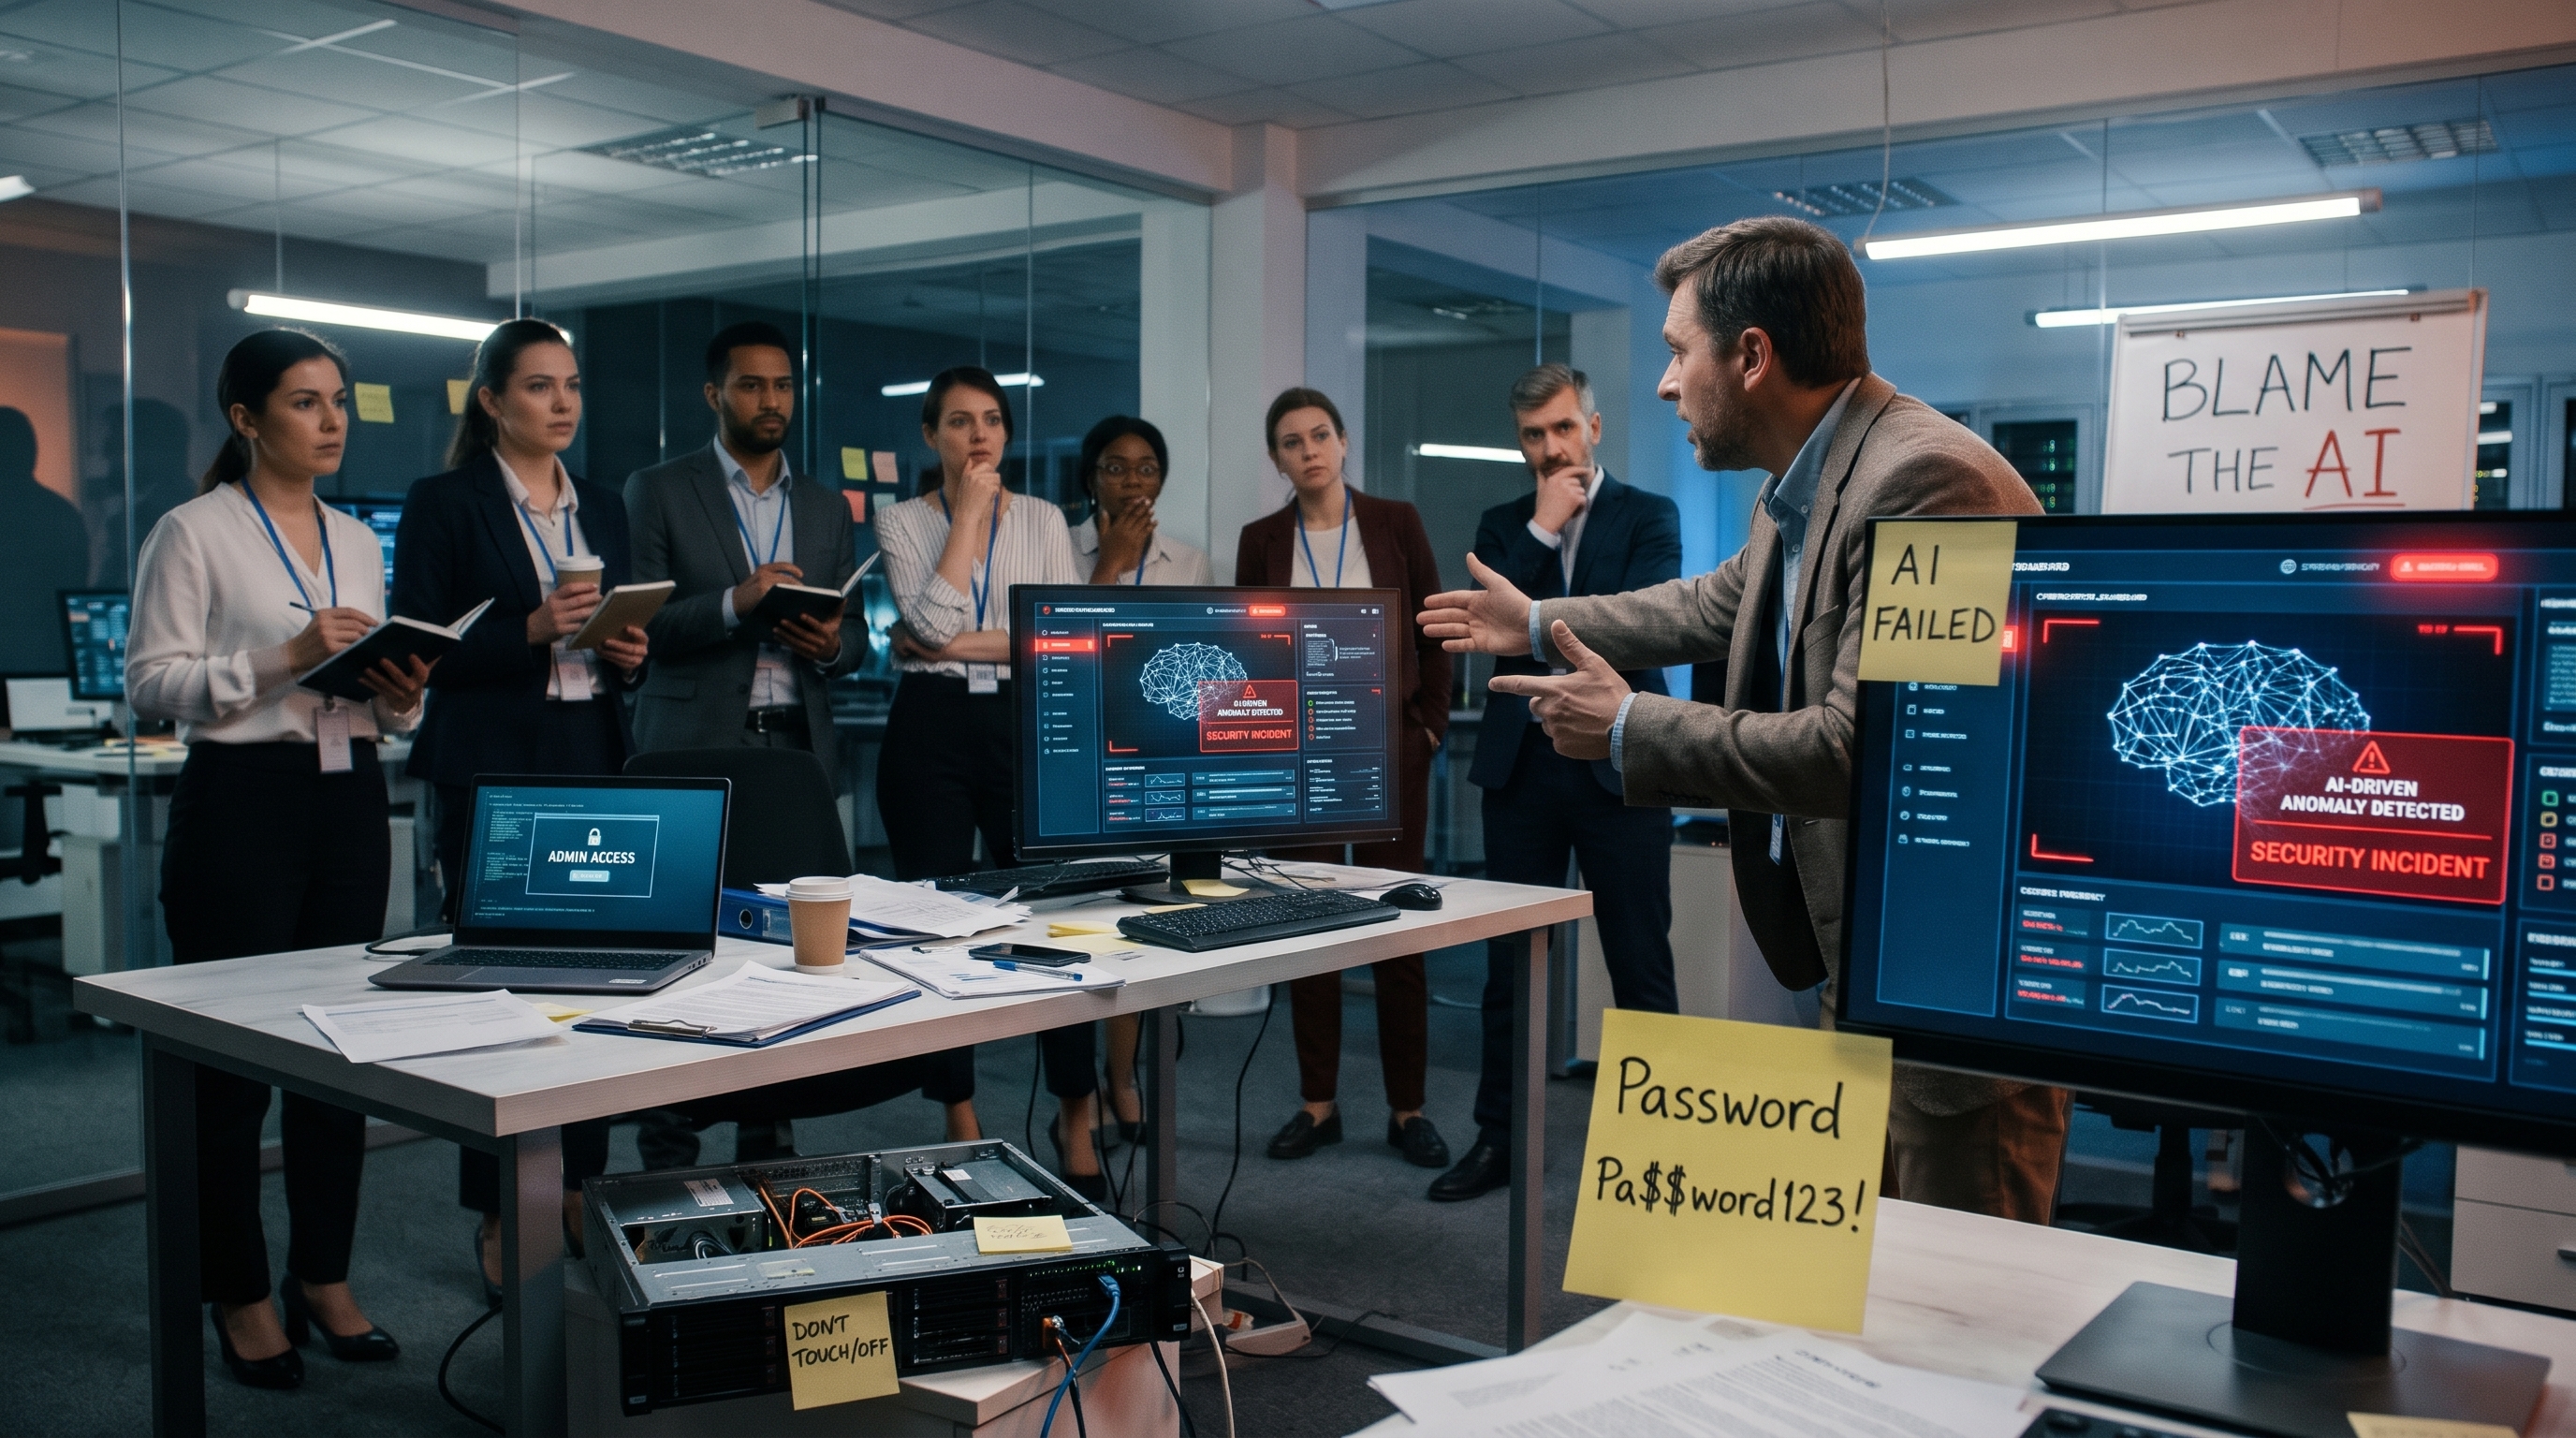
I believe that AI is a convenient ‘scapegoat’ for systemic issues across the tech landscape. And here’s why…
▪ Governance of cybersecurity and AI is thin. IBM’s 2025 breach study and the 2025 Marsh Cyber Risk Intelligence Center report both establish that organizations with weak governance and oversight controls tend to be breached more often and pay the most. In my experience, a poor tone from the top is the biggest reason for cybersecurity failures.
▪ Many companies, even the large and well-resourced ones, are simply doing bad security. The basics such as asset management, endpoint protection, configuration management, continuous vulnerability management, IAM, incident response, secure software development, third-party risk management, etc. are routinely ignored or poorly executed. Verizon’s 2026 report puts vulnerability exploitation at 31% of initial access, up from 20% and ahead of phishing and credential abuse. Remediation rates have also worsened.
▪ Software is built for velocity, not secure by design. Agile development and automation aren’t the villains, but they’re key contributors if not done right. But shipping code without security gates is definitely the main culprit (and way too many companies are doing this). Veracode’s 2026 report analyzed 1.6 million applications. 82% of organizations carry security debt, up 11% on last year. Debt meaning known flaws left open for more than a year. 60% carry critical debt (severe, exploitable flaws unresolved for over a year), up 20% year on year.
▪ AI-generated code is fast, not safe. Veracode’s 2026 tests show AI-generated code passing security checks only 56% of the time, with no improvement. It’s also getting bloated and duplicated. Bloat enlarges the attack surface and hides flaws. Duplicated code is harder to audit and find vulnerabilities.
▪ AI agents aren’t going rogue. We’re giving them excessive permissions and autonomy and then not governing them. That’s a design and oversight failure, not Skynet-type science fiction. OWASP’s Excessive Agency risk names excessive functionality, permissions and autonomy as the root causes for agentic-related breaches.
▪ Regulation is lagging. Secure by design is voluntary, and the EU AI Act’s high-risk rules just slipped to 2027–28. Voluntary doesn’t work; it’s a market failure. Constantly delayed regulation is a problem because AI companies keep shipping more features and functionality in the gap (and thus the possibility for harm increases exponentially).
AI doesn’t create these weaknesses. It accelerates them, at machine speed.
The answer isn’t slower AI. It’s boards that own the risk, least privilege for agents, secure-by-default pipelines, and regulation that actually gets enforced.